
CISM Certification Eligibility: The 5-Year Experience Requirement and How Waivers Actually Work
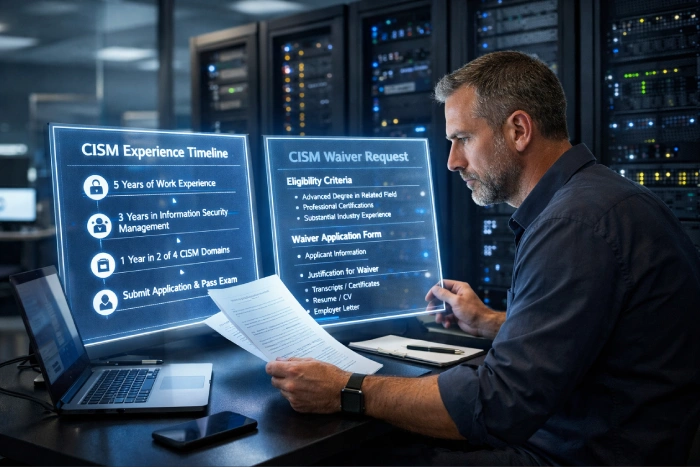
There are five years of experience required to become a certified CISM information security management professional: three out of four CISM domains and at least five years of professional information security management experience. There is a possibility of waiving up to two years of the experience requirement if certain credentials or education requirements are met, but the experience at management level is still required. Another key factor is that there are no prerequisites to sit the CISM exam. ISACA offers the option for candidates to take the CISM exam for me first and then apply for certification based on experience.
The Two-Layer Structure of CISM’s Experience Requirement
The most important thing to know about CISM eligibility is to split the total experience requirement from the management experience that is actually eligible. ISACA currently has a five-year information security management work experience requirement in the five job practice areas.
Consider eligibility in two ways:
- Overall experience: 5 Years, Qualifications: Professional Experience
- Domain coverage: At least 3 out of the 4 domains of experience: CISM1, CISM2, CISM3, and CISM4.
This distinction is important since it’s not enough to have five years of technical IT or cybersecurity experience; one must also have this experience within the context of Information Security Management. The work of a professional in information security management recognised by ISACA must match their responsibilities.
The four focuses of CISM are information security governance, information security risk management, information security program development and management and information security incident management.
This guide to the most difficult professional certification exams ranked also allows you to make comparisons with CISM.
What Actually Counts as “Management” Experience
CISM management experience is not a binary choice between having or not having the word “manager” in your job title. A job title alone may not be the most relevant responsibility for security governance, security risk, security programs, security controls or incident management.
For instance, a person who is referred to as a security analyst could be very accountable for the security programme or risk activities. On the other hand, a person who holds the title of manager might not have sufficient information security management experience.
So, your experience should be expressed in real-world responsibilities and projects. Keep good records of employers, dates, roles, and responsibilities for verification as part of the certification application.
Howthe Waiver Actually Works (And What It Doesn’t Reduce)
The CISM waiver will decrease overall experience burden but not make unrelated experience CISM experience. According to the latest ISACA guidance, substitutions and waivers can shorten the five-year requirement by up to two years.
Depending on the current ISACA rules, certain professional credentials or education may apply. There’s a practical reason for this: the maximum reduction time is two years, so it is not realistic to expect a candidate to have more than one credential for the same time period to remove experience.
Review a candidate with a qualifying credential which offers a maximum of two years of reduction. This candidate can have 3 years of qualifying professional experience in information security management rather than 5 years. The rest of the experience must meet ISACA’s requirements and the appropriate CISM work areas.
The ISACA certification policies may change; check the latest application guidance against your waiver category before using it.
You Can Take the CISM Exam Before You Meet the Experience Requirement
It is possible to sit for the CISM exam prior to acquiring the necessary professional experience. Just passing the exam does not necessarily make you CISM certified; experience and application requirements must be met as well.
This is a convenient choice for those who are still starting their career in the professional sector. Qualifying experience can be obtained while studying and passing the exam.
ISACA currently allows candidates 5 years from the date that they pass the exam to take the certification exam. This required work experience shall be accrued in the 10 years before the certification application is filed.
That makes the CISM exam before experience route particularly advantageous if you are sure that your career trajectory will soon give you the remaining experience needed to meet the qualification requirements.
What Happens During Application Verification
ISACA asks candidates to provide proof of their professional experience to apply for certification. Experience must be substantiated, and your application should include accurate information about experience and responsibility.
Before applying, organise:
- The name of the employer and the date of employment
- Job titles and responsibilities
- Relevant security projects
- CISM domains covered
- Verification details for supervisor/manager
Avoid making up several years of employment history until the application time. Clean records will make it easier to move into certification.
A Quick Eligibility Self-Check
Before planning your certification, make sure to verify 4 factors:
- Have relevant experience in Information Security Management?
- Have at least three CISM domains in your experience?
- May the required experience be waived?
- Do you work within the time frame of ISACA’s scope of application?
If you don’t know the answer to one, refresh yourself with the latest ISACA requirements before deciding if you are eligible or not.
FAQ
Q: How many years of experience do I need for CISM?
In general, CISM will require 5 years of information security management experience in at least 3 of 4 CISM domains, as appropriate, or be waived.
Q: Can a CISSP waive the CISM experience requirement?
ISACA allows the CISM experience requirement to be waived for a qualifying CISSP credential. Please refer to the current eligibility information, as applicable substitutions may be subject to change.
Q: Can I take the CISM exam before I have enough experience?
Yes. The CISM exam can be taken and passed prior to meeting experience requirements, and the certification application can be submitted within five years of passing.
Q: Does the CISM management experience requirement have a waiver?
ISACA recognises some experience substitutions or waivers; however, candidates are still required to meet the relevant professional information security management requirements as per current certification requirements.
Q: How does ISACA verify CISM work experience?
Yes. ISACA may request experience verification, so be sure to have accurate records of your employment and a qualified supervisor or independent verifier who can verify your experience.
Closing CTA Guidance
When you break the ‘years of experience’ from the actual type of security management that you did, eligibility for CISM can become more easily determined. If you are able to determine what type of experience is acceptable, you are aware of any possible waiver, and you are able to schedule the exam to fit your career, then you may be closer to certification than you realise. Once you are sure whether you are eligible or not, you can concentrate on practising for the exam itself. For more help, contact Bypass My Exam’s CISM exam help or reach out to the team regarding your preparation issues.